
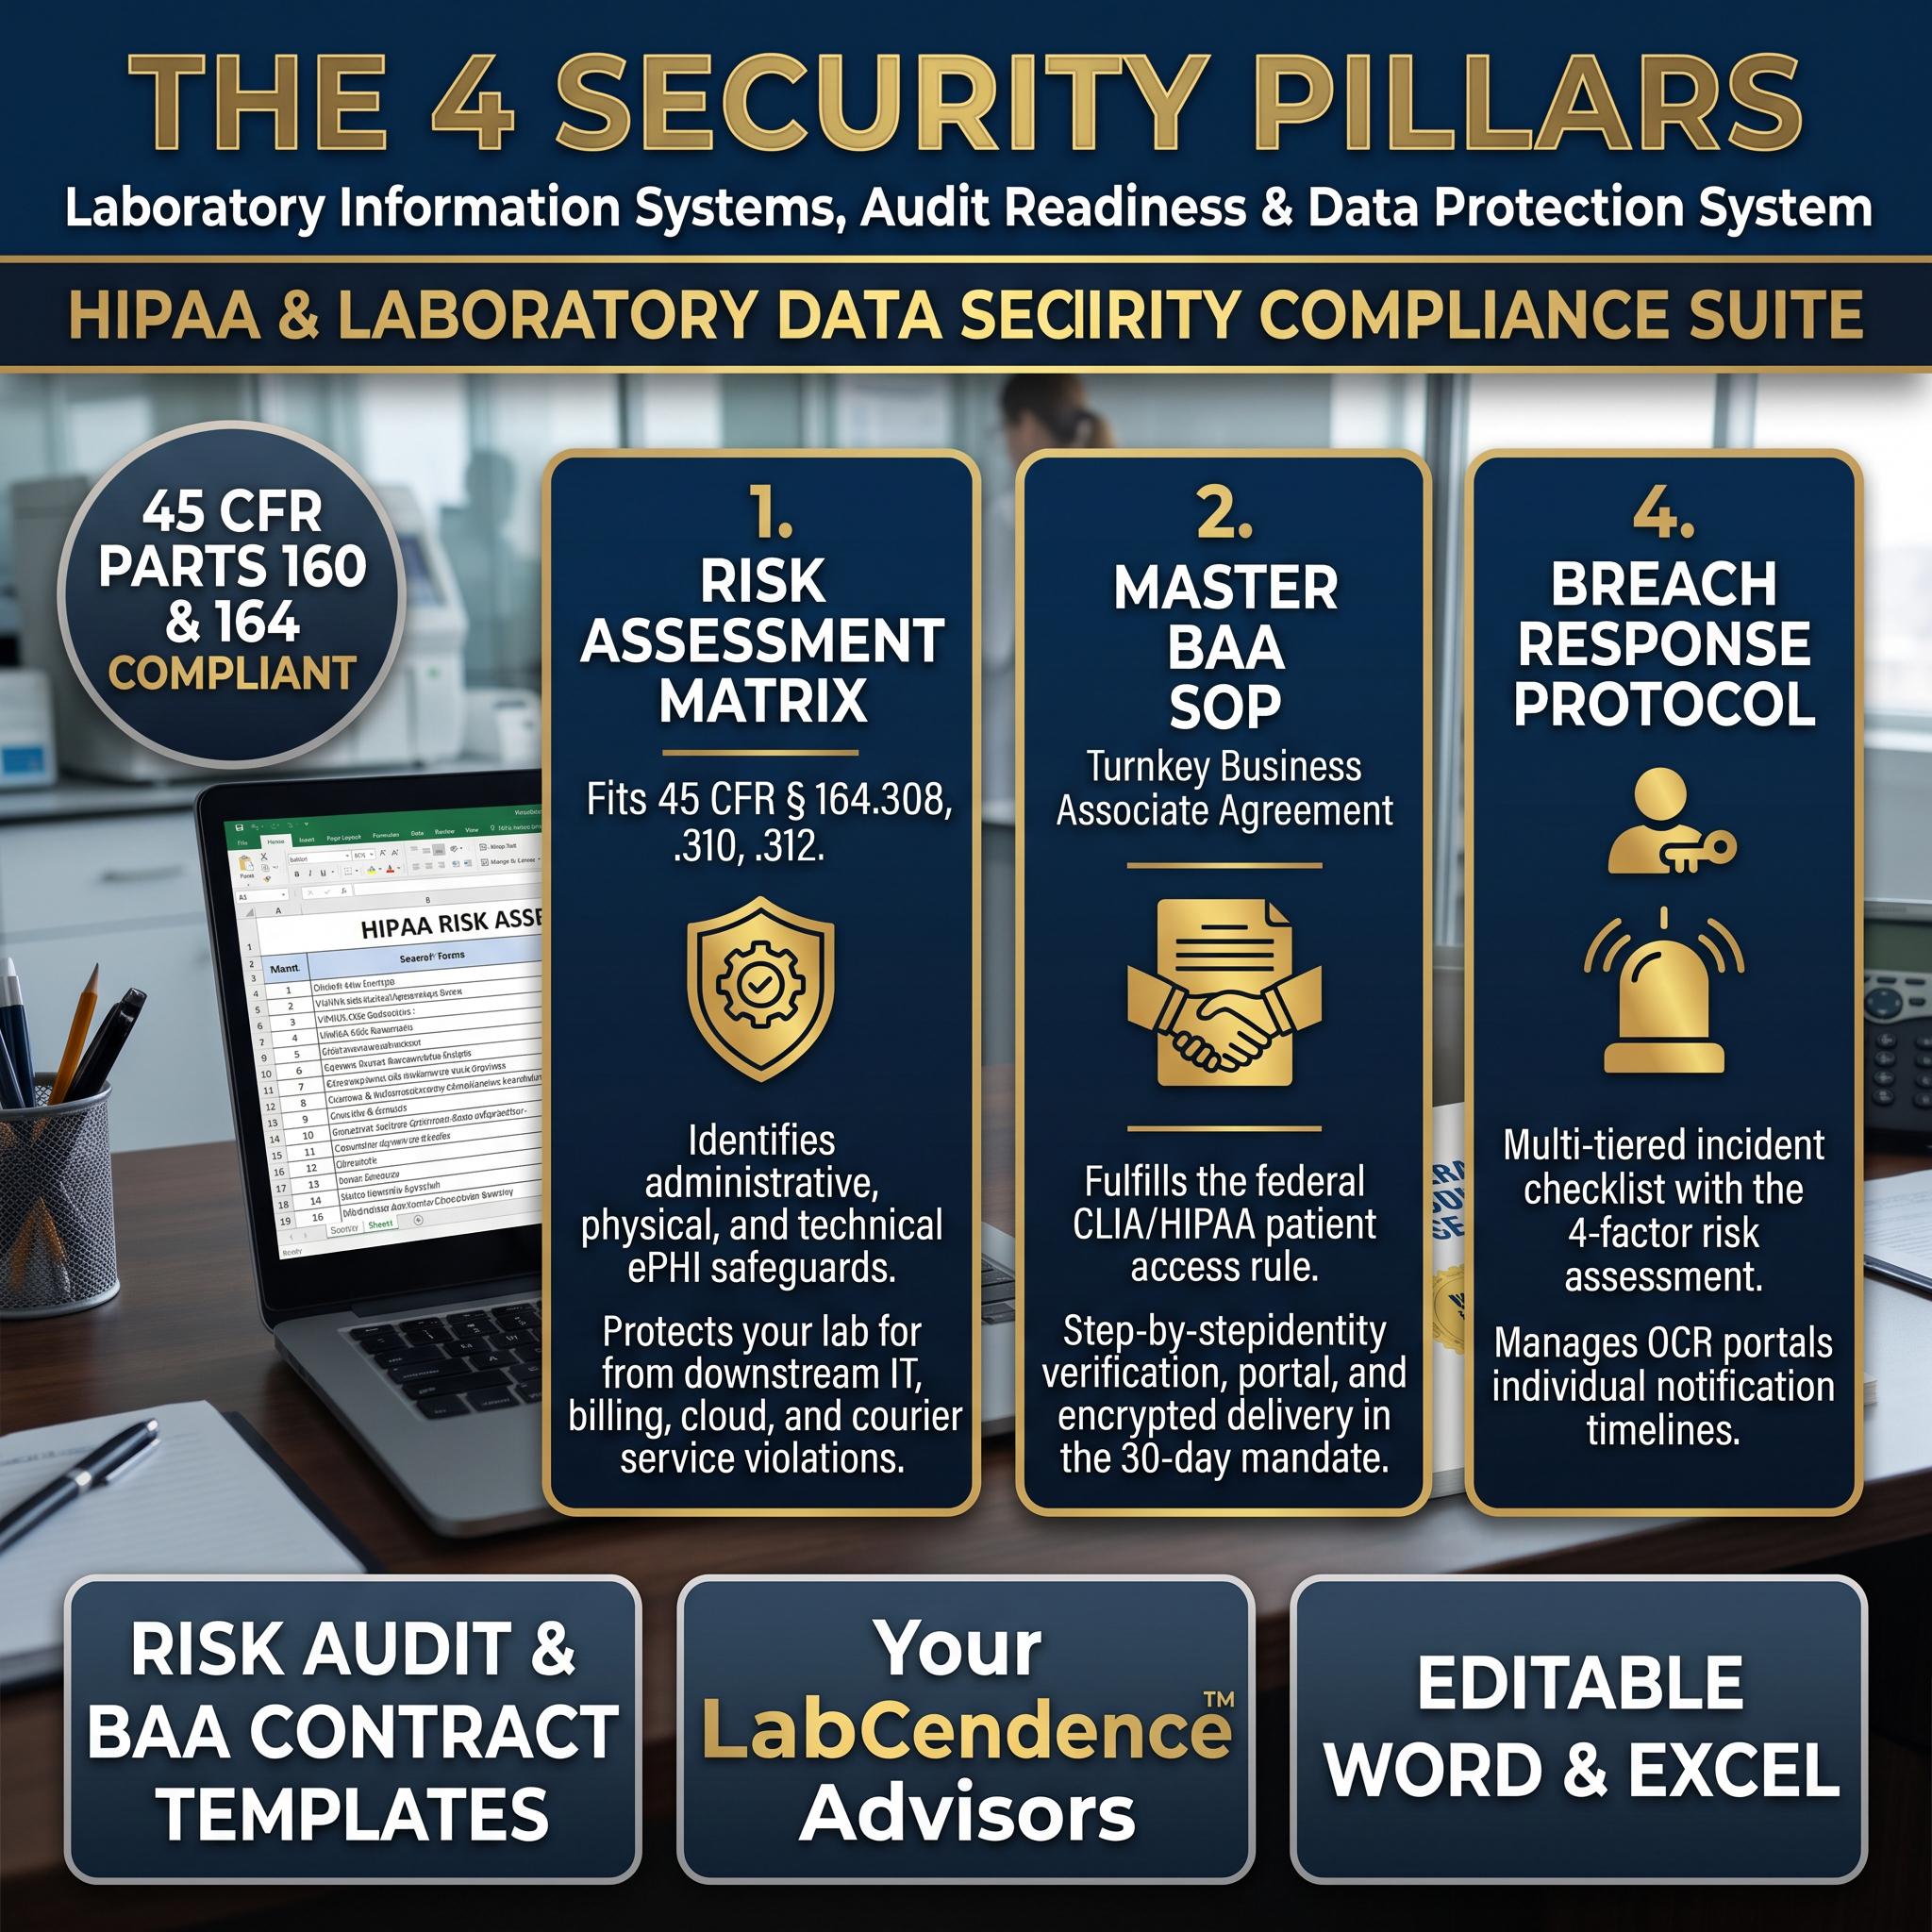
HIPAA & Laboratory Data Security Compliance Manual: LIS Risk Assessment, Vendor Contracts in Word, Excel, PDF
$247.00
★ CLINICAL LABORATORY HIPAA & DATA SECURITY COMPLIANCE MASTER MANUAL ★
By Your LabCendence™ Regulatory Advisors
The Turnkey HIPAA Privacy, Security Rule Risk Assessment, Direct Patient Access & Vendor BAA System for Clinical Laboratories.
Value: $247.00
Formats: Fully Editable Microsoft Word (.docx) + Automated Microsoft Excel (.xlsx) + Print-Ready PDF (.pdf)
Large-Print Optimized: Formatted with generous 12.5pt typography and padded layouts for clear, effortless binder printing.
Clinical laboratories handle some of the most sensitive protected health information (PHI) in healthcare: diagnostic test orders, infectious disease results, molecular sequences, clinical toxicology panels, and electronic health record (EHR/LIS) interfaces.
During CLIA surveys, CAP General Checklist inspections (GEN.40000+), and federal HHS Office for Civil Rights (OCR) audits, inspectors demand proof of a comprehensive HIPAA Security Rule Risk Assessment, active Business Associate Agreements (BAAs) with every IT vendor, and formal protocols for the CLIA Direct Patient Result Access Rule.
A single unencrypted workstation, a missing courier BAA, or an unlogged privacy misdirection can trigger statutory OCR civil monetary penalties ranging from $137 to $68,928 per violation (up to $2.06M annually).
Healthcare cybersecurity attorneys charge upwards of $3,500 to $7,500 to draft lab privacy manuals. The Clinical Laboratory HIPAA & Data Security Compliance Master Manual provides your Laboratory Director, Privacy Officer, and IT Administrator with an institutional, audit-tested compliance architecture built from 35+ years of clinical laboratory survey leadership.
━━━━━━━━━━━━━━━━━━━━
WHAT’S INCLUDED IN THIS COMPLIANCE SYSTEM
━━━━━━━━━━━━━━━━━━━━
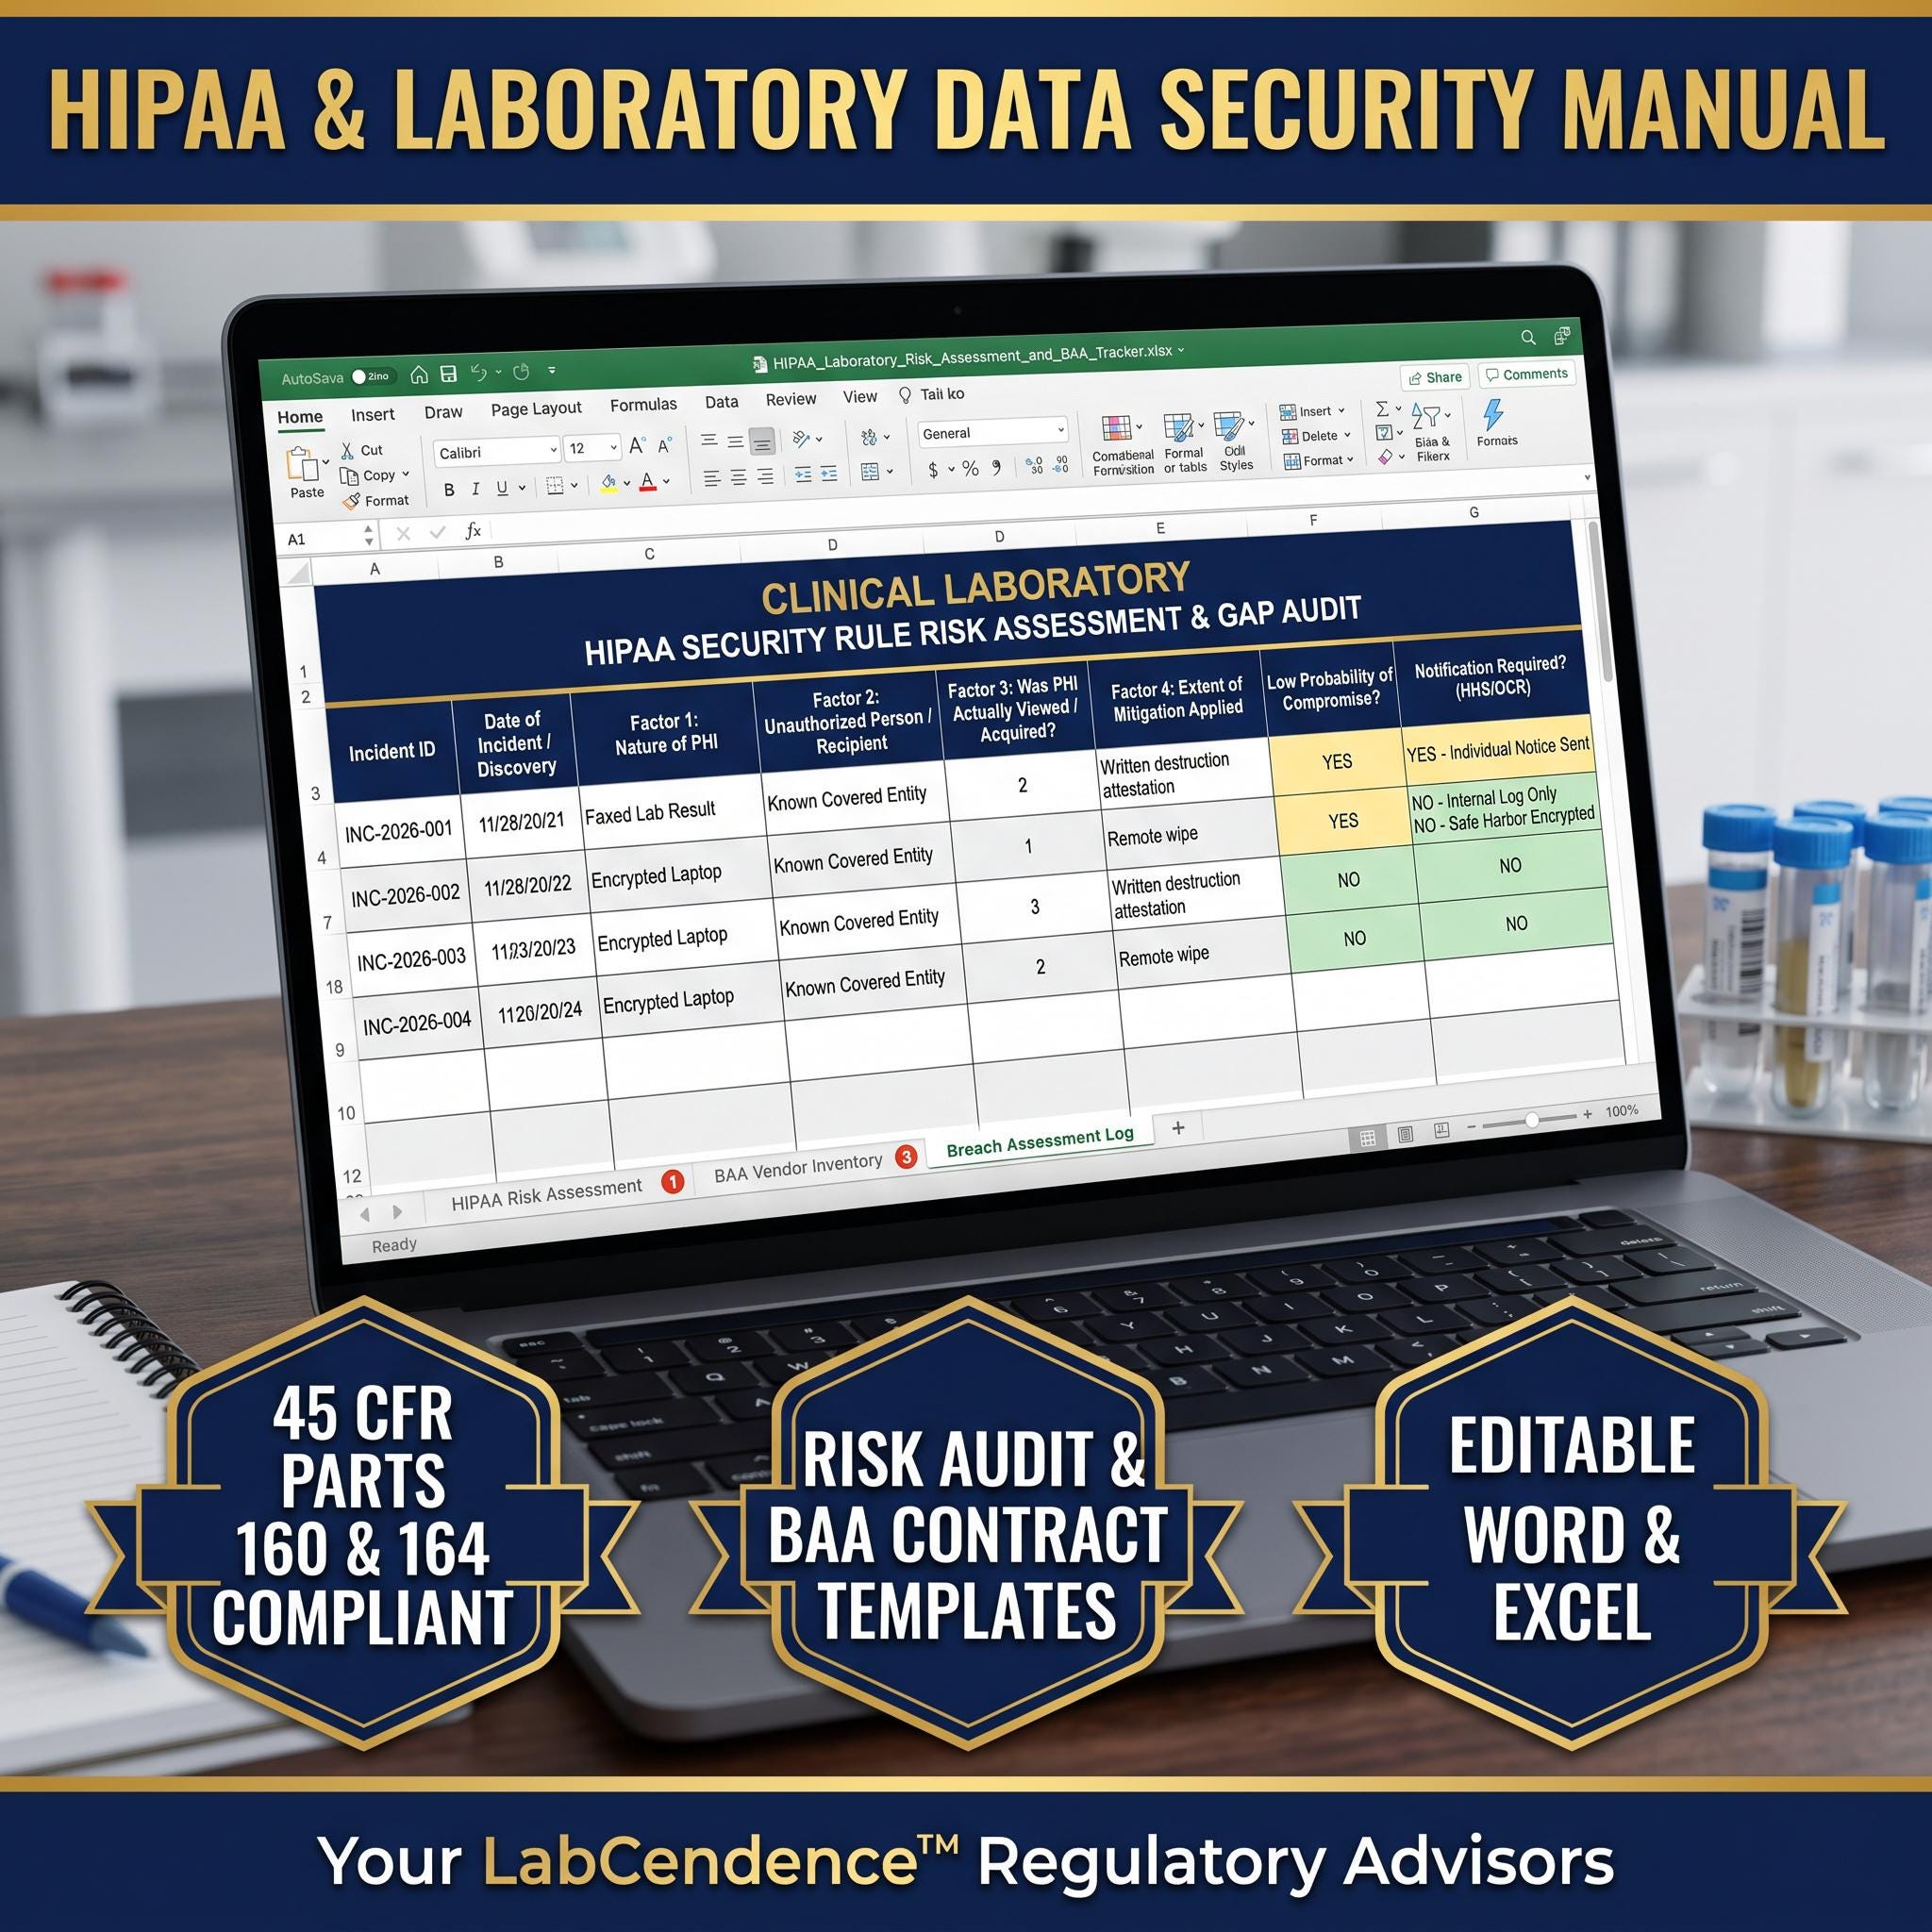
1. MASTER HIPAA RISK ASSESSMENT & BAA TRACKER (.XLSX)
A multi-tab, automated Microsoft Excel command center built to 45 CFR Part 164 standards:
• Tab 1: HIPAA Security Rule Risk Assessment Matrix: Comprehensive gap audit covering Administrative Safeguards (training, policies), Physical Safeguards (accessioning door access, 5-minute auto-locks, media destruction), and Technical Safeguards (unique logins, MFA, immutable audit trails, TLS 1.3 / AES-256 encryption).
• Tab 2: Master Business Associate Agreement (BAA) Vendor Inventory: Centralized tracking for Cloud LIS providers, billing services, courier networks, cloud hosts, shredding contractors, and reference send-out laboratories.
• Tab 3: HIPAA Four-Factor Breach Risk Assessment Log: Statutory risk analysis evaluating the nature of PHI, unauthorized recipients, actual viewing/acquisition, and mitigation to determine if HHS OCR / patient breach notification is legally mandated.
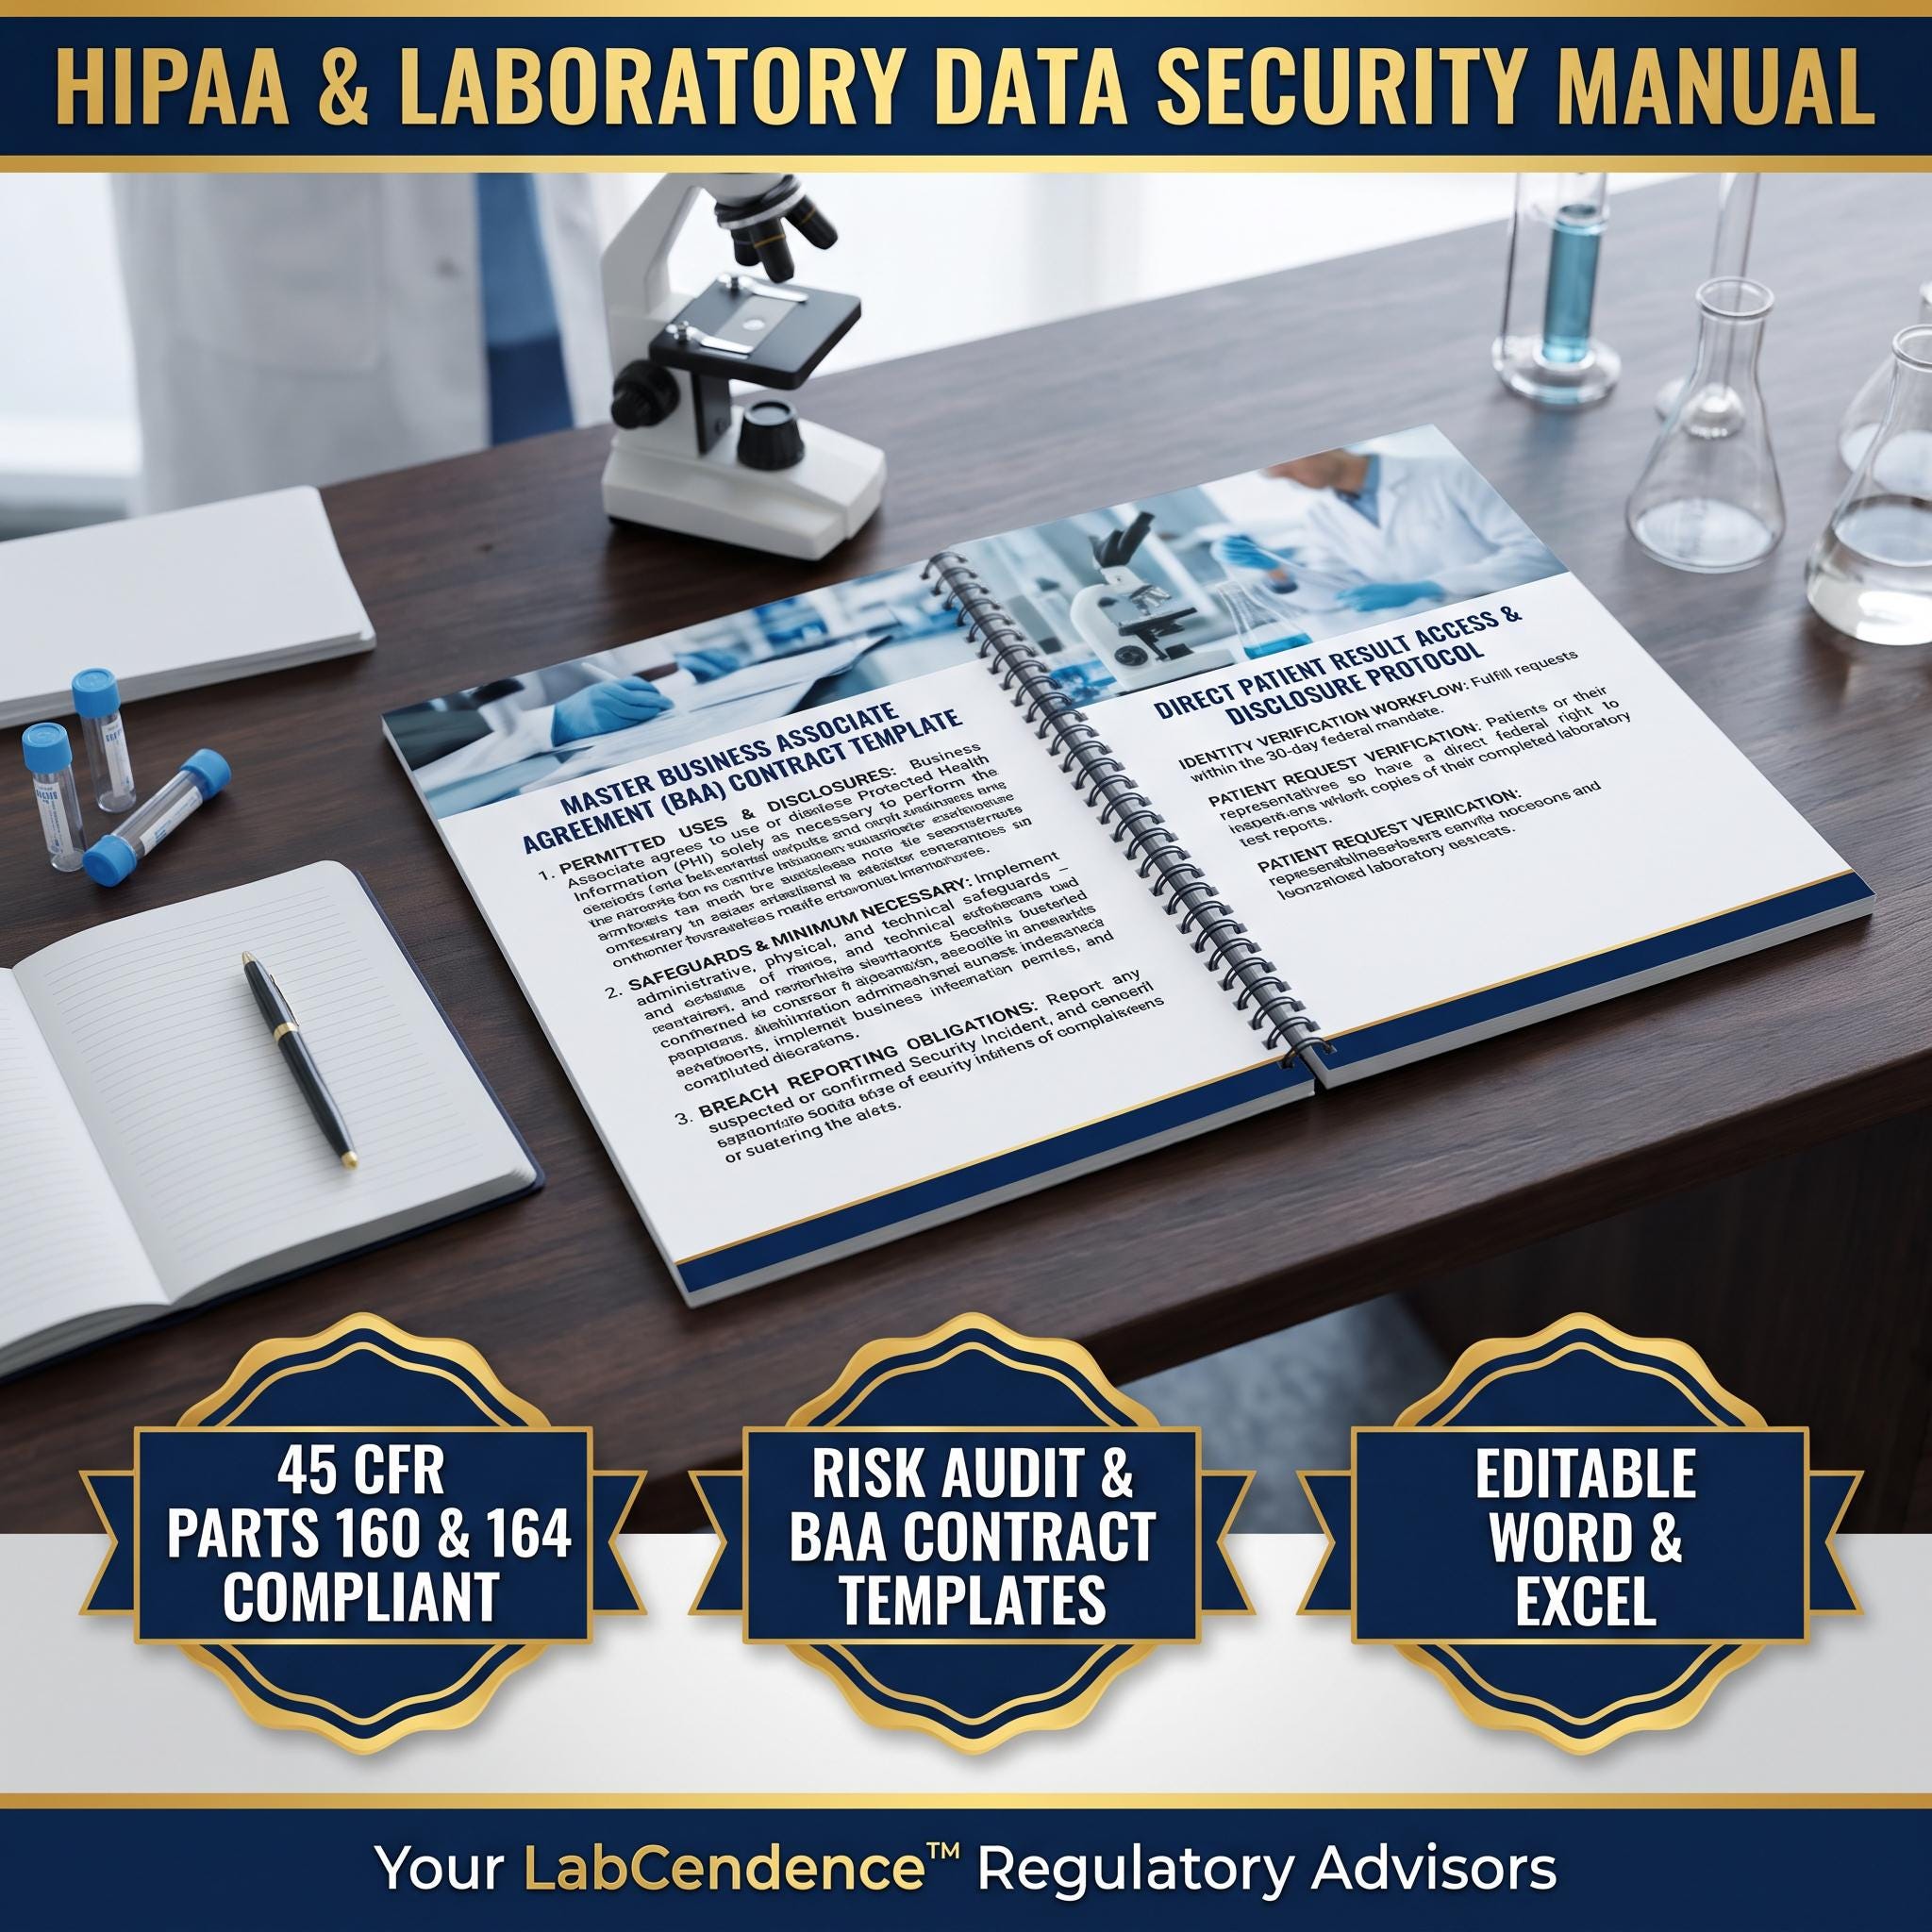
2. MASTER HIPAA & DATA SECURITY COMPLIANCE MANUAL (.DOCX)
An exhaustive, 6-section operational manual and institutional policy binder:
• Section 1.0: Clinical Laboratory HIPAA Privacy & Security Policy (Minimum Necessary standard, workforce role-based permissions).
• Section 2.0: Administrative, Physical & Technical Safeguards (Workstation hygiene, clean desk rules, password complexity, encryption protocols).
• Section 3.0: Direct Patient Result Access Protocol (Complete alignment with the CLIA/HIPAA Final Rule granting patients direct report access within 30 days without physician barrier).
• Section 4.0: Master Business Associate Agreement (BAA) Contract Template (Legal contract ready for signature with third-party LIS, billing, and IT vendors).
• Section 5.0: Four-Factor Breach Risk Assessment & Incident Response Playbook (60-day notification timelines, mitigation workflows, OCR portal reporting).
• Section 6.0: Annual Regulatory Review & Medical Director Approval Block (Multi-tier sign-off for Privacy Officer, Security Officer, and Laboratory Medical Director).
3. CUSTOMER ONBOARDING & SETUP ARCHITECTURE GUIDE (.PDF)
A large-print executive guide detailing officer appointments, workforce training schedules, annual risk assessment rhythms, and inspection binder staging.
━━━━━━━━━━━━━━━━━━━━
REGULATORY STANDARDS SATISFIED
━━━━━━━━━━━━━━━━━━━━
• HIPAA Privacy Rule: 45 CFR Part 160 and Part 164, Subparts A and E
• HIPAA Security Rule: 45 CFR Part 164, Subpart C (§ 164.308, § 164.310, § 164.312)
• Breach Notification Rule: 45 CFR Part 164, Subpart D (§ 164.400 - § 164.414)
• HITECH Act: Subtitle D Privacy and Security Enforcement Amendments
• CLIA / HIPAA Final Patient Access Rule: 45 CFR § 164.524 & 42 CFR § 493.1291 (Direct Patient Access to Completed Test Reports)
• CAP Accreditation: General Laboratory Checklist (GEN.40000+ Information Management & Security)
━━━━━━━━━━━━━━━━━━━━
APPLICABLE TESTING FACILITIES
━━━━━━━━━━━━━━━━━━━━
• Independent Clinical Laboratories (Reference, STAT, Regional)
• Molecular Diagnostic & PCR Testing Centers
• Clinical Toxicology & Pain Management Facilities
• Physician Office Laboratories (POLs) & Group Practice Labs
• Mobile Phlebotomy & Specimen Collection Organizations
━━━━━━━━━━━━━━━━━━━━
TECHNICAL SPECIFICATIONS & DELIVERY
━━━━━━━━━━━━━━━━━━━━
• Formats: Fully Editable Microsoft Word (.docx), Automated Microsoft Excel (.xlsx), and Print-Ready PDF (.pdf)
• Large-Print Designed: 12.5pt body text and generous cell padding for clear physical binder printing
• Clean ZIP Delivery: Instant digital download without confusing internal listing numbers
• Turnkey & Unlocked: Pre-formatted brackets for your laboratory's legal name, CLIA ID, and designated officers
Digital downloads
File delivery
Your files will be available to download once payment is confirmed.
Payment Options
Returns & Exchanges
Returns & exchanges not accepted
But please contact me if you have problems with your order
Privacy policy
LabCendenceTemplates Privacy Policy
Effective October 11, 2026
WHO I AM
I am Maria , the individual owner of LabCendenceTemplates, based in United States. I am responsible for how I use buyer information in operating this shop. For privacy questions or requests, contact me through Etsy Messages.
INFORMATION I USE
I use information Etsy makes available to me about your purchase, including your name, username, contact information, order details, and messages you send me. I do not receive your full payment-card details.
PURPOSES AND LEGAL BASES
I use this information to fulfill purchases and provide support as necessary to perform our purchase agreement. I may also use it to meet legal obligations and for legitimate business interests, such as resolving disputes and preventing fraud, where those interests do not override your rights.
STORAGE AND SHARING
I keep buyer information within Etsy. I do not export it to customer spreadsheets, mailing lists, or separate customer databases. I do not sell buyer information or use it for unsolicited marketing.
I share information with Etsy as needed to manage orders and resolve problems. I may disclose information to authorities when legally required.
RETENTION
I use buyer records only for as long as needed to fulfill orders, provide support, resolve disputes, and meet applicable recordkeeping obligations. These needs determine the retention period for information under my control. Etsy independently controls how long its platform retains transaction records and messages; I cannot promise deletion of records Etsy must retain.
INTERNATIONAL PROCESSING
I access this shop from the United States. Etsy’s own storage, international transfers, and platform processing are governed by its privacy policy, available at https://www.etsy.com/legal/privacy.
YOUR RIGHTS
Depending on applicable law, you may request access, correction, deletion, restriction, or portability of your information, or object to certain uses. These rights may be subject to legal exceptions. You may also complain to your local data protection authority.
Contact me through Etsy Messages about information I control. For information controlled by Etsy, contact Etsy through its Privacy Policy or Help Center. I will address requests concerning my own use of your information.
SENSITIVE INFORMATION
Please do not send patient records, test results, genetic information, Social Security numbers, or other sensitive personal information. These are not needed to purchase or use this shop’s digital resources.
CHANGES
I will update this policy if my information-handling practices change.